Remotely Access Any Deployment Cell (Kubernetes Cluster) with Omnistrate's Secure CLI
Omnistrate is revolutionizing how service providers manage and interact with their deployment cells. A new feature that now provides a secure and standardized way to remotely access the Kubernetes API of any deployment cell (Kubernetes Cluster). This capability eliminates the need for complex networking configurations or additional permissions in the target account.
This new functionality allows you to securely connect to any Kubernetes cluster, whether it's running in your own cloud account, a customer's account, or across different cloud providers and regions.
Key Benefits
- Simplified Operations: Gain direct access to any managed Kubernetes cluster with a single command. This removes the need for bastion hosts, VPNs, or managing separate credentials for each environment, dramatically simplifying day-to-day operations.
- Standardized Cross-Channel Management: Whether you're debugging an issue in a development cluster or a production instance running in a customer's environment, the process is identical. This standardization reduces complexity and the risk of human error.
- Enhanced Security: All connections are established over a secure mTLS (mutual TLS) channel using reverse tunneling. This means you don't need to expose the Kubernetes API server to the public internet or open inbound firewall ports in the target account. Access is further protected by short-term tokens, ensuring a robust Zero Trust security model.
- Seamless Tool Integration: Your existing Kubernetes tooling, including
kubectl,k9s, andhelm, works out-of-the-box. Once the secure connection is established, you can use your preferred tools to manage and inspect your applications and services.
How It Works: Secure by Design
Remote deployment-cell access through your control plane is designed for security and simplicity. When you initiate a remote session, the following happens:
- Secure Tunneling: A secure reverse tunnel is created from your local machine to the target Kubernetes cluster. This connection is protected with mTLS, ensuring that both the client and server authenticate each other's identity through trusted certificates.
- Dynamic Configuration: The Omnistrate CTL (
omnistrate-ctl) dynamically updates your localkubeconfigfile with temporary, short-lived credentials for the target cluster. - Direct API Access: With the
kubeconfigupdated,kubectland other Kubernetes-native tools can securely communicate with the cluster's API server through the mTLS tunnel.
This architecture ensures that access is granted on-demand and is automatically revoked, without ever exposing the cluster's control plane to external threats.
Getting Started: A Step-by-Step Guide
Interacting with your remote clusters is straightforward using the Omnistrate CLI.
Step 1: List Your Deployment Cells
To see all the deployment cells you manage, run the following command (More details):
omnistrate-ctl deployment-cell list

+----------------+-------------------------------+----------------------+----------------------------+---------------------------------------------+--------------+-------------+---------+------------+
| CLOUD_PROVIDER | CURRENT_NUMBER_OF_DEPLOYMENTS | CUSTOMER_EMAIL       | CUSTOMER_ORGANIZATION_NAME | HEALTH_STATUS                               | ID           | REGION      | STATUS  | TYPE       |
+----------------+-------------------------------+----------------------+----------------------------+---------------------------------------------+--------------+-------------+---------+------------+
| azure          |                             1 | <nil>                | <nil>                      | Status: UNKNOWN | Entities: 0/0 healthy     | hc-example01 | eastus2     | FAILED  | Kubernetes |
| gcp            |                             4 | <nil>                | <nil>                      | Status: HEALTHY | Entities: 556/556 healthy | hc-example02 | us-central1 | RUNNING | Kubernetes |
| aws            |                             2 | <nil>                | <nil>                      | Status: HEALTHY | Entities: 195/195 healthy | hc-example03 | us-east-1   | RUNNING | Kubernetes |
| aws            |                             1 | <nil>                | <nil>                      | Status: HEALTHY | Entities: 139/139 healthy | hc-example04 | us-west-2   | RUNNING | Kubernetes |
| aws            |                             0 | <nil>                | <nil>                      | Status: UNKNOWN | Entities: 0/0 healthy     | hc-example05 | ap-south-1  | FAILED  | Kubernetes |
| aws            |                             1 | [email protected] | Example Customer           | Status: HEALTHY | Entities: 242/242 healthy | hc-example06 | us-east-1   | RUNNING | Kubernetes |
+----------------+-------------------------------+----------------------+----------------------------+---------------------------------------------+--------------+-------------+---------+------------+
Step 2: Connect to a Remote Cluster
To establish a secure session with a specific deployment cell, use the update-kubeconfig command. You will need the ID of the deployment cell from the list in the previous step. If the cluster belongs to a customer, you will also need their email address. More details
omnistrate-ctl deployment-cell update-kubeconfig hc-example06 --customer-email [email protected]
This command will securely update your local kubeconfig file. The path to the updated configuration will be displayed in your terminal.
You can also specify a custom path for the kubeconfig file:
omnistrate-ctl deployment-cell update-kubeconfig hc-example06 --customer-email [email protected] --kubeconfig /path/to/custom/kubeconfig
Step 3: Interact with Your Cluster
You are now securely connected to the remote Kubernetes cluster. You can use your favorite tools to manage your applications. For example, you can list the namespaces in the cluster:
# Set the KUBECONFIG environment variable to the path provided by the previous command
export KUBECONFIG=/tmp/kubeconfig

# Use kubectl to interact with the cluster
# Check if you can create pods in the current namespace
kubectl auth can-i create pods
no

# Check if you can create pods in a specific namespace
kubectl auth can-i create pods --namespace=kube-system
no
By default, the kubeconfig will assume a read-only cluster-wide role (cluster-reader). If you need to perform administrative tasks, you can specify a different role:
omnistrate-ctl deployment-cell update-kubeconfig hc-example06 --customer-email [email protected] --role cluster-admin
You can also use tools like k9s for a more interactive terminal UI to manage your cluster's resources, view logs, and much more, all through the secure Omnistrate tunnel.
Manage Just-in-Time Access
Just-in-time (JIT) access adds an approval policy, temporary grants, revocation, and lifecycle auditing to the secure deployment cell connection described above.
Before you begin
You need the following:
- The latest
omnistrate-ctl, authenticated to the SaaS Provider organization. - Root access to configure the approval policy.
- Root or Admin access to view deployment cell access requests. For manual approval, your user must also be selected as an approver.
Omnistrate stores the policy in the environment used by your organization for deployment cells. The console and CLI resolve the applicable GLOBAL or PROD environment automatically. Specify --environment-type GLOBAL or --environment-type PROD only when you need to select one explicitly.
Choose an approval mode
| Mode | Behavior |
|---|---|
Automatic (AUTO) | Omnistrate approves new requests automatically for 60 minutes. No approver list is retained. |
Manual (MANUAL) | A selected Root or Admin user must approve each request. The approver can grant access for 11 to 720 minutes; omitting a duration uses the backend default. |
Changing the mode affects existing requests:
- Changing from automatic to manual approval immediately invalidates active grants and disconnects their access streams. New requests require approval.
- Changing from manual to automatic approval denies pending requests. Requesters must rerun the CLI command. Existing approved grants keep their current expiration time.
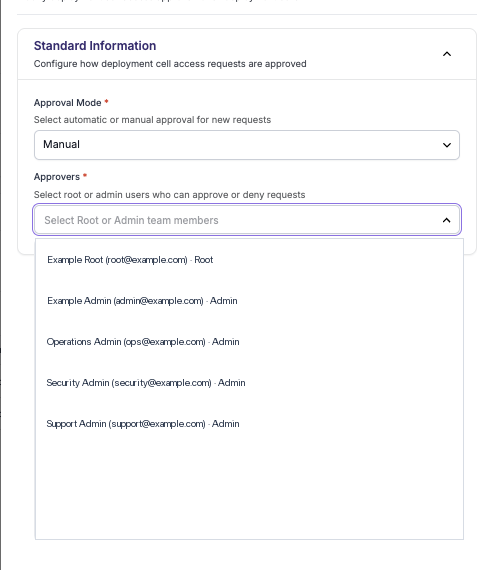
Configure the approval policy in the console
- Open Governance Center > Deployment Cell Access.
- Select Modify Approval Policy.
- Select Automatic or Manual.
- For manual approval, select one or more Root or Admin users as approvers.
- Save the policy.
Configure the approval policy with the CLI
View the effective policy:
Require manual approval by one or more users:
omnistrate-ctl access-request config set \
  --approval-mode MANUAL \
  --approver-email [email protected] \
  --approver-email [email protected]
Restore automatic approval:
The config set command reads the persisted policy after updating it and displays the effective configuration. When the mode is AUTO, the displayed approver list should be empty.
Request access when manual approval is enabled
Include a reason when requesting access under manual approval:
omnistrate-ctl deployment-cell update-kubeconfig hc-example06 \
  --customer-email [email protected] \
  --reason "Investigate deployment health"
The command creates or reuses an access request and waits for an approver. If you interrupt it, rerun the same command to reuse the request after it is approved.
Review access requests
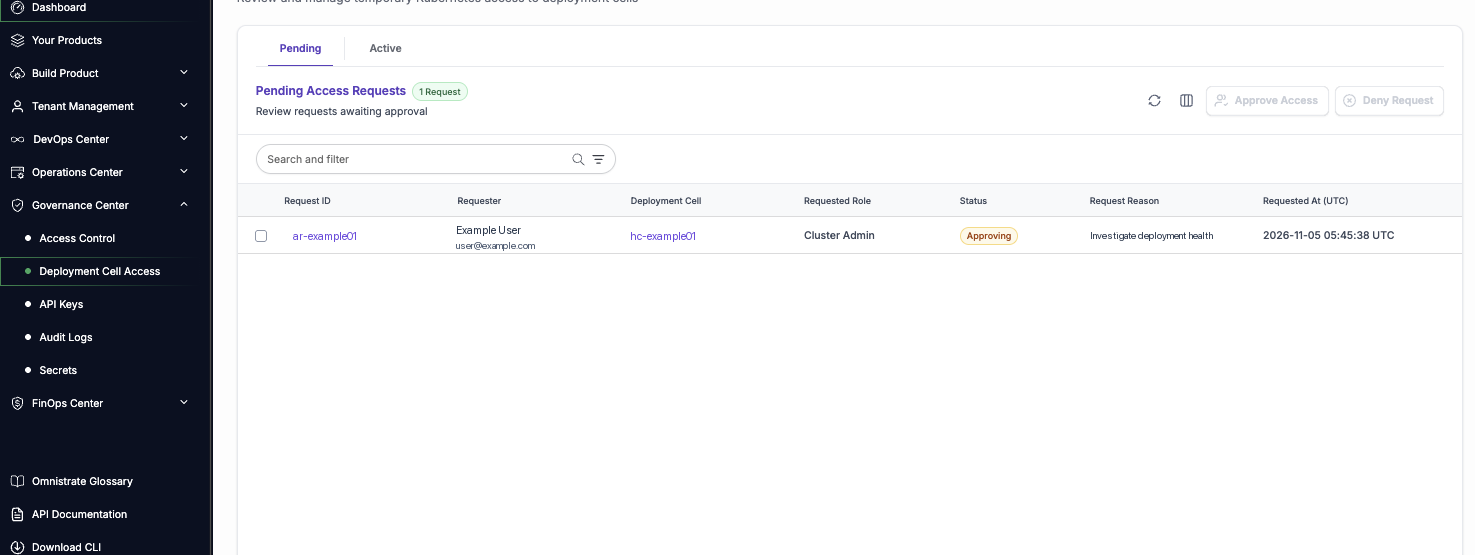
In the console, open Governance Center > Deployment Cell Access. The Pending tab shows requests awaiting a decision, including requests transitioning to approval.
Use the CLI to list all currently visible requests:
The default list contains all live requests without a limit. It also includes denied, revoked, and expired requests from the last 24 hours; this recent terminal portion is limited to the newest 1,000 records for overflow protection.
Filter the list by one or more lifecycle statuses:
omnistrate-ctl access-request list --status PENDING,APPROVING
omnistrate-ctl access-request list --status APPROVED,REVOKING
omnistrate-ctl access-request list --status DENIED,REVOKED,EXPIRED
Inspect one request in detail:
Approve or deny a request
Selected approvers can approve or deny pending requests from the console. Select a request in the Pending tab, then choose Approve Access or Deny Request.
To approve a request with the backend's default duration:
To grant a specific duration from 11 to 720 minutes:
To deny a request:
Review and revoke active access
The Active tab shows approved grants, their roles, approvers, reasons, and expiration times.
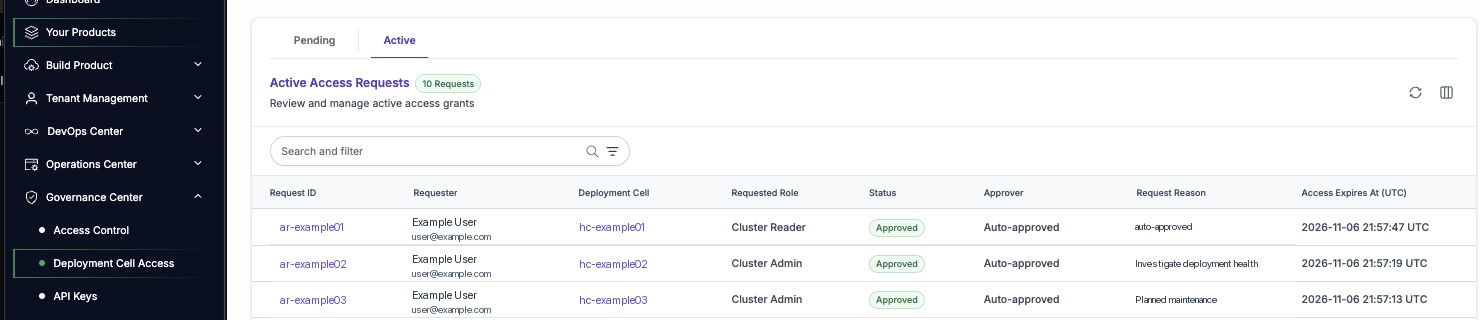
When manual approval is enabled, a selected approver can revoke a grant before it expires:
Revocation disconnects the active stream and invalidates the grant. Otherwise, access ends automatically when the approved duration expires. Automatic grants cannot be manually revoked from the console; change the policy to manual approval if you must invalidate all automatic grants immediately.
Audit JIT access
Open Governance Center > Audit Logs to review request, approval, denial, revocation, and expiration events, including who performed each human action. Filter the date range and expand an event to inspect its request details.
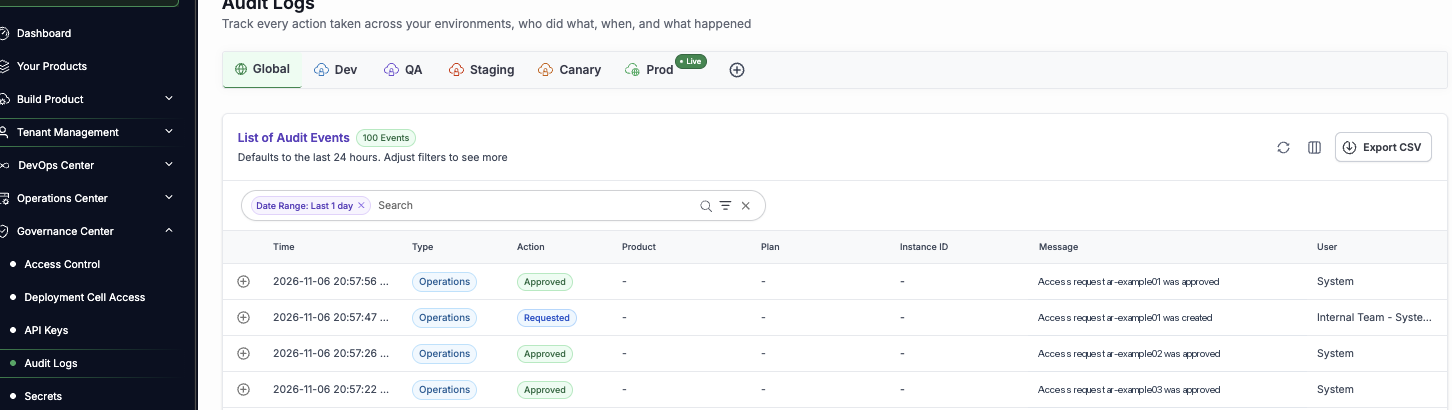
To retrieve JIT access events with the CLI:
The environment filter is optional. Add --environment-type GLOBAL or --environment-type PROD only when you want to restrict the results to that environment. You can also use --start-date and --end-date with RFC 3339 timestamps to limit the audit interval.
JIT access guidance
- Grant
cluster-readerunless the task requires administrative changes. - Require a specific reason for manual requests and choose the shortest practical approval duration.
- Select multiple approvers to avoid blocking urgent work when one approver is unavailable.
- Revoke access when work finishes before the approved expiration time.
- Review JIT access events regularly and protect generated kubeconfig files as temporary credentials.
Troubleshoot JIT access
- The request remains pending: Confirm that manual approval is enabled and that a configured approver has selected the request. Rerun
update-kubeconfigafter approval if the original command was interrupted. - The request was denied after changing to automatic mode: Pending manual requests are denied during the mode change. Run
update-kubeconfigagain to create an automatically approved request. - The CLI cannot find a recently revoked or expired request: Run
access-request listor filter by its terminal status. Terminal requests remain visible for 24 hours, subject to the newest-1,000-record safety limit. - Multiple cells match the identifier: Add
--customer-email [email protected]to identify the customer-owned deployment cell. - The policy shows approvers in automatic mode: Run
omnistrate-ctl access-request config set --approval-mode AUTO, then confirm the persisted policy withconfig get. Automatic mode should have no approvers.
Deployment Cell Bootstrap Visibility
When Omnistrate provisions a new deployment cell (Kubernetes cluster), you can monitor the bootstrap process and troubleshoot failures through the Operations Center.
Debug events
If a deployment cell fails to provision or encounters errors during bootstrap, Omnistrate surfaces debug events that help you identify the root cause:
- Bootstrap failures: Errors during cluster creation (e.g., quota limits, permission issues)
- Add-on failures: Issues with required Kubernetes add-ons or drivers
- Network configuration errors: Problems with VPC or subnet setup
- Cloud provider errors: API errors or resource limits from the underlying cloud provider
You can view these events in the Operations Center workflow details for the specific deployment cell provisioning operation.
Tip
If a deployment cell bootstrap fails, check the workflow details for specific error messages. Common causes include cloud account quota limits, missing IAM permissions, or network CIDR conflicts.